 how-to
Automating KYC Compliance for Autonomous Software Agents
Table of Contents
- Why Autonomous Software Agents Break Traditional KYC Models
- What You'll Need Before You Start
- AI Agents for KYC Verification: Defining Agent Identity and Delegation
- Step-by-Step: Building an Agentic KYC Workflow
- Step 1: Map the KYC Lifecycle to Agent Actions
- Step 2: Bind Each Agent to a Verified Principal
- Step 3: Set Authorization Gates Before Consequential Actions
- Step 4: Build Human-in-the-Loop Exception Handling
- Step 5: Threat-Model the Agent Before Launch
- Step 6: Define Operational Metrics Before Go-Live
- Step 7: Deploy in Stages and Monitor Continuously
- KYC Automation Tools and the Agent Execution Trust Stack
- The AI Agent Audit Trail: Logging, Attribution, and Rollback
- Threat Modeling and Testing Your Agentic KYC Controls
- Common Mistakes to Avoid When Automating KYC Compliance
- Frequently Asked Questions
Last Updated: October 8, 2026
Why Autonomous Software Agents Break Traditional KYC Models
Traditional KYC compliance assumes a human fills out the form.
Here is the core problem. A know your customer program verifies a person, checks their documents, screens them against watchlists, and assigns a risk score.
That gap is why automating KYC compliance for autonomous software agents is now a distinct discipline rather than an extension of ordinary onboarding automation.
The stakes are rising. The FFIEC BSA/AML Examination Manual treats customer due diligence as a risk-based obligation, and an agent acting on a customer's behalf still sits inside that obligation.
So what does an agent-native KYC model actually look like? It has three parts: a verified agent identity, a scoped delegation from a real customer, and a tamper-evident record of every action. We cover each below, plus a step-by-step build.
What You'll Need Before You Start
A successful build starts with prerequisites, not code.
**1. The FFIEC BSA/AML Examination Manual expects risk-based customer due diligence, and an agent acting on a customer's behalf still sits inside that obligation.
**2.
3. A verified principal behind every agent. No agent should exist without a proven human or business identity.
4. A policy engine that evaluates rules before an action runs. Prompts are not policy engines.
5. A tamper-evident logging system. Logs must capture inputs, policy decisions, outputs, and the human reviewer when one is involved.
6. A named human reviewer for escalated exceptions. Escalation without an owner stalls.
**7.
8. A test environment with synthetic identities. You cannot safely test agent behavior against live customer data.
A common pattern is to treat these eight items as a readiness gate: no agent goes to production until every item is signed off by both the compliance owner and the engineering owner.
AI Agents for KYC Verification: Defining Agent Identity and Delegation
AI agents for KYC verification are software actors whose identity, permissions, and authority are cryptographically bound to a verified human or business principal. That binding is what makes them auditable.
Think of it as three layers:
- Principal identity. The verified customer, proven through standard identity verification and proof of identity checks.
- Agent identity. A unique, signed credential for the software itself, tied to a specific code version.
- Delegation scope. A written limit on what the agent may do, for how long, and up to what value.
Delegation is where most programs fail. A customer might authorize an agent to submit applications but not to open accounts.
The NIST AI Risk Management Framework frames this as mapping, measuring, and managing risk across an AI system's lifecycle, which is exactly the discipline agent identity needs.
Accountability follows the same chain.
Step-by-Step: Building an Agentic KYC Workflow
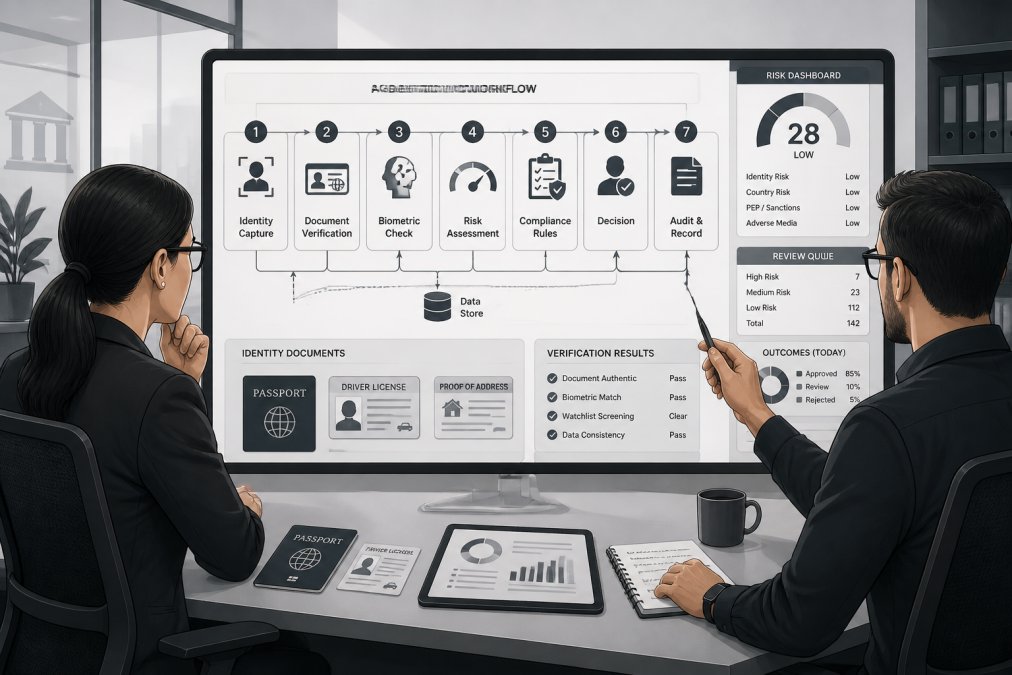
An agentic KYC workflow replaces manual handoffs with agent actions, while keeping a human in the loop for anything consequential. Most approaches stop at "map the lifecycle, add gates, escalate exceptions." That is the easy part.
Step 1: Map the KYC Lifecycle to Agent Actions
List every stage of onboarding, then mark which stages an agent can handle. Typical candidates:
- Document ingestion and data extraction from identity documents
- Data validation against customer-supplied details
- Sanctions screening and watchlist screening
- Risk scoring and initial risk assessment
- Case creation for anything that fails a check
Keep account opening decisions with a human until your controls are proven. For each stage, note the data source, the expected latency, and the failure mode if the agent gets it wrong.
Step 2: Bind Each Agent to a Verified Principal
Before an agent touches a workflow, create a delegation record that ties it to a verified human or business. The record should include:
- The principal's verified identity reference
- The agent's unique credential and code version
- The permitted actions (read, write, submit, move funds)
- Value and volume limits
- Expiration date and renewal conditions
- The named human who can revoke the delegation
If the delegation lives only in a prompt, it is not a control. It is a suggestion. Store it where the policy engine can read it at execution time.
Step 3: Set Authorization Gates Before Consequential Actions
Define which actions need a second approval. A gate should fire before the action, not after.
Explore Ecosystem Government Contracting →
- Moving funds above a set threshold
- Changing a customer's verified details
- Submitting a filing to a regulator
- Overriding a failed screening result
- Onboarding a new counterparty
Each gate should require a signed authorization from the principal or a designated officer, and the authorization should be logged with the payload it approved.
Step 4: Build Human-in-the-Loop Exception Handling
No agent gets everything right. Design exception handling first, not last.
- Route low-confidence extractions to manual review
- Route screening hits to a case management queue
- Cap the number of retries before escalation
- Log every escalation with the reason and the reviewer
A workflow that cannot escalate cleanly will either stall or push bad decisions through.
Step 5: Threat-Model the Agent Before Launch
Run a structured adversarial pass. Test at minimum:
- Prompt injection. Can a crafted document make the agent skip a screening step?
- Scope creep. Can the agent act outside its delegation without triggering a gate?
- Replay. Can a previously approved payload be resubmitted?
- Identity spoofing. Can a rogue agent impersonate a trusted one?
- Document manipulation. Can a modified ID pass extraction and validation?
Feed the system hostile inputs and confirm the gates hold. Repeat after every code change.
Step 6: Define Operational Metrics Before Go-Live
You cannot manage what you do not measure. Set baselines for:
- False-positive rate on screening hits
- Manual review rate per 1,000 onboarding attempts
- Median and 95th-percentile processing time
- Completion rate for legitimate applicants
- Audit exceptions per quarter
- Escalation-to-resolution time
Track these weekly for the first quarter, then monthly. A rising false-positive rate usually means a data source drifted; a rising review rate usually means the policy engine is too strict.
Step 7: Deploy in Stages and Monitor Continuously
Start with a read-only agent, then a low-value write agent, then a full-permission agent. Each stage should run for a full business cycle before you expand scope. Continuous monitoring means re-screening against watchlists on a schedule, re-checking delegation validity, and alerting on anomalous action patterns.
KYC Automation Tools and the Agent Execution Trust Stack
KYC automation tools handle the document and screening work. They do not, on their own, prove that an agent was authorized to act. That is a separate layer.
It can be thought of as a trust stack with four rungs:
| Layer | What It Does | What It Proves |
|---|---|---|
| Identity | Verifies the human or business principal | Who the customer is |
| Verification | Checks agent code and workflows before deployment | What the agent can do |
| Authorization | Approves the payload at the point of execution | That this action was allowed |
| Attribution | Records the outcome and economic value | What happened and who owns it |
Most teams have the first layer and assume the rest. The gap is the second and third rungs.
This is where we build. AI Modularity secures autonomous AI at the point where trust matters most: execution. Our Agent Verify™ checks agent code and workflows before they run, while A2SPA™ authorizes payloads at the moment of execution.
The AI Agent Audit Trail: Logging, Attribution, and Rollback
An AI agent audit trail is a tamper-evident record of every agent action, its authorization, and its outcome. Without one, you cannot answer a regulator's questions or a board's.
What to log for each action:
- The agent identity and code version
- The principal and delegation scope in force
- The input payload and the policy decision
- The result, including any error or rejection
- The timestamp and the reviewer, if a human was involved
Attribution matters as much as logging. If an agent generates economic value, you should be able to trace that value to a principal and a task.
Retention rules vary by obligation. The SEC recordkeeping requirements set expectations for books and records in regulated finance, and agent logs should meet the same bar.
Threat Modeling and Testing Your Agentic KYC Controls
Threat modeling asks one question: how would this agent be abused? Run it before launch and again after every change.
Test these scenarios:
- Prompt injection. Can a crafted document make the agent skip a screening step?
- Scope creep. Can the agent act outside its delegation without triggering a gate?
- Replay. Can a previously approved payload be resubmitted?
- Identity spoofing. Can a rogue agent impersonate a trusted one?
Adversarial testing should be routine, not a one-time exercise. Feed the system hostile inputs and confirm the gates hold.
Common Mistakes to Avoid When Automating KYC Compliance
Four mistakes account for most failures in KYC compliance programs that add agents.
- Treating the agent as the customer. The principal is the customer. The agent is an instrument.
- Putting controls in prompts. Prompts are not policy engines. Enforce limits in code.
- Skipping continuous monitoring. Onboarding is a moment. Ongoing due diligence is a process.
- Logging outcomes but not decisions. You need the "why," not just the "what."
Fix these and your program holds up under review.
Automating KYC compliance for autonomous software agents is hard because trust has to live at execution, not in a policy document. AI Modularity was built for exactly this gap. Agent Verify™ validates agent behavior and permissions before deployment, A2SPA™ authorizes consequential actions at the point they run, and A2EA™ attributes outcomes after execution, all on chain-agnostic infrastructure that fits enterprise and government operations. Get started with AI Modularity and deploy autonomous agents with verifiable security and accountability.
Frequently Asked Questions
How can autonomous software agents support KYC compliance?
Autonomous software agents support KYC compliance by handling document ingestion, data extraction, identity verification, sanctions screening, and risk scoring at machine speed. They can process thousands of customer onboarding records per day, flag exceptions, and route edge cases to human reviewers. The key is to constrain each agent to a defined scope, authorize consequential actions before they execute, and log every decision for audit. This reduces manual review backlogs while keeping a human-in-the-loop for high-risk decisions.
How do you verify an AI agent before it handles customer data?
Verification starts before deployment. Review the agent's code, model weights, permissions, and data access scope against a written policy. Test it in a sandbox with synthetic identity documents and known sanctions lists to confirm it behaves as expected. Use cryptographic signing to bind the agent's identity to its authorized actions, so any tampering is detectable. Only after the agent passes adversarial testing and risk assessment should it touch live customer data. This approach aligns with the execution trust model used in regulated industries.
What controls should an agentic KYC workflow include?
An agentic KYC workflow should include pre-execution authorization gates, real-time data validation, sanctions and watchlist screening, risk scoring thresholds, human-in-the-loop escalation for exceptions, and an immutable audit trail. Each agent action should be attributable to a specific agent identity, with delegation rules that define what the agent can and cannot do. Continuous monitoring and ongoing due diligence keep the workflow compliant as customer risk profiles change. Rollback procedures handle failures without leaving the case in an inconsistent state.
How do you audit actions taken by an autonomous compliance agent?
Build an AI agent audit trail that captures every action, decision, input, and output with a timestamp and cryptographic signature. The trail should link each action to the agent's identity, the authorization that permitted it, and the customer record it affected. Store logs in a tamper-evident system so regulators and internal auditors can reconstruct the decision path. Regular audits should test whether the trail is complete and whether any actions occurred outside authorized scope. This supports regulatory compliance and case management reviews.